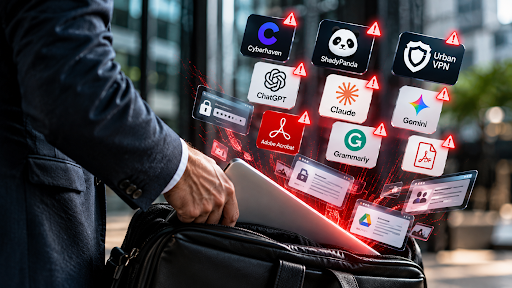
Chrome extension security is the browser risk that most IT providers ignore. Your staff have probably installed dozens of add-ons without asking anyone. In fact, some of those add-ons can read every page your team opens.
When we run Google Workspace risk assessments at Sentry Cyber, we check the Google Admin console first. We often find hundreds of extensions and apps linked to employee accounts. By default, users can install whatever they like, and nobody keeps watch.
This guide explains the risks to Chrome extension security in plain English. It also shares real news stories and a simple plan to take back control. Best of all, you can follow the Google Admin console steps today.
Why Chrome Extension Security Matters for Your
Business
A Chrome extension is a small program that adds features to your browser. For example, popular ones include password managers, grammar checkers, PDF tools and VPNs. They feel harmless because they live in the Chrome Web Store.
However, many extensions ask to read and change data on every website you visit. That includes Gmail, your banking portal and your accounting software. In other words, a single extension can see everything your staff see.
Extensions can also steal session cookies. Therefore, an attacker may skip your password and multi-factor authentication completely. The cookie proves the user already logged in, so the attacker walks straight into the account.
Extensions also update themselves silently. As a result, a safe tool today can turn harmful after one update. Good Chrome extension security covers the whole life of an extension, not just the first install.
Chrome Extensions vs Chrome Apps: What Is the Difference?
First, extensions change how Chrome behaves. Chrome apps were different because they ran like standalone programs. Google has largely retired traditional Chrome apps, so extensions now carry most of the risk.
Even so, the Google Admin console still groups apps and extensions together. Staff can also add web apps and connect third-party apps to their Google accounts. Each connection is another door into your data, so you need to review all of them.
What We Find During Google Workspace Risk
Assessments
Many IT providers skip browser extensions during security reviews. Instead, they focus on firewalls, patching and email filtering. Unfortunately, the browser is where your staff do most of their work.
When Sentry Cyber audits a Google Workspace environment, we open the apps and extensions report in the Admin console. Most businesses are surprised by what appears. Typically, we see these problems:
- Staff install free VPNs, PDF converters and AI assistants without approval.
- Nobody reviews permissions or checks who owns each extension.
- Duplicate and abandoned extensions pile up over time.
- IT teams cannot say which extensions are safe, because nobody ever looked.
Consequently, the business carries a risk it cannot even measure. Our Google Workspace security services start by closing this Chrome extension security gap.
Real Cases Where Browser Extensions Caused
Serious Problems
These risks are not theoretical. In fact, news outlets have reported major incidents every year. Here are four recent examples of poor Chrome extension security.
The Cyberhaven Supply Chain Attack
In December 2024, attackers phished a Cyberhaven employee who had access to the Chrome Web Store. They then published a malicious version of the company’s own extension. The Hacker News reported that at least 35 extensions were compromised, exposing over 2.6 million users.
The lesson is simple. A trusted publisher can still be hijacked, so you must keep checking trust over time.
Shady Panda and the Extensions That Turned Bad
Koi Security uncovered a long-running campaign called ShadyPanda. Its extensions behaved normally for years. Then they received malicious updates. Researchers say the campaign hit about 4.3 million Chrome and Edge users. The Register explained that the updates arrived through the browsers’ own trusted auto-update system.
Urban VPN Proxy and Stolen AI Conversations
In late 2025, researchers found that Urban VPN Proxy was capturing chats with AI tools. Those tools included Chat GPT, Claude and Gemini. The extension carried a Google Featured badge and millions of users. Dark Reading reported that about eight million users were affected.
Imagine your staff pasting client details into an AI tool while that extension runs. That is exactly why extension control matters.
Fake Workday and NetSuite Tools in 2026
In January 2026, BleepingComputer reported five malicious extensions posing as tools for Workday, NetSuite and SAP SuccessFactors. According to Socket researchers, they stole login data and blocked security pages. Although only 2,300 installs were reported, stolen business credentials can fuel ransomware attacks.
How to Improve Chrome Extension Security With an
Allowlist
The best fix for Chrome extension security is also the simplest. Switch from allowing everything to using an allowlist. Many people call this a whitelist, while Google calls it an allowlist. Only approved extensions can be installed, and everything else stays blocked.
Google Workspace even lets staff request new extensions. Your IT team then reviews each request and does the research before saying yes. As a result, staff keep a path to the tools they need, and you keep control.
Step-by-Step: Set Up the Allowlist in the Google Admin
Console
Follow these steps in the Admin console. Google changes menu names now and then. If a label looks different, check Google’s guide to allowing or blocking apps and extensions.
- Sign in to admin.google.com with an administrator account.
- Go to Devices > Chrome > Reports > Apps & extensions usage to see everything currently installed.
- Decide which extensions your business truly needs.
- Go to Devices > Chrome > Apps & extensions > Users & browsers and choose your organisational unit.
- Add each approved extension from the Chrome Web Store and set its installation policy to Allow install.
- Open the Allow/block mode setting and choose Block all apps, admin manages allowlist, users may request extensions.
- Review staff requests under Devices > Chrome > Apps & extensions > Requests, then allow or block each one.
First, always audit before you switch the mode. Otherwise, you may break a tool your team relies on. Google also explains the request process in its extension workflows guide.
How to Vet an Extension Request
Staff send requests to IT, so IT must check each one. Use this quick checklist before you approve anything:
- Who publishes the extension, and can you verify the company?
- Does it need permission to read all websites?
- Has the owner or developer changed recently?
- Does the privacy policy explain what data it collects?
- Do the reviews look genuine, and is the install count sensible?
- Can a built-in Google Workspace feature do the same job?
Additionally, you can block extensions by permission. You can also stop extensions from altering sensitive webpages. Both options sit in the Admin console.
Push Out the Extensions Your Business Needs
An allowlist works best when you also install the right tools for everyone. Force-install extensions from the Admin console, and staff will not hunt around the Chrome Web Store. Consequently, fewer people go looking for risky alternatives. This approach also strengthens your wider Chrome extension security plan.
Good candidates for a force install include:
- A password manager extension, such as Keeper or LastPass.
- The Office editing extension, which opens Microsoft Office files in Google Docs, Sheets and Slides.
- A reputable ad and content blocker, such as uBlock Origin Lite.
To do this, open Apps & extensions > Users & browsers and add the extension from the Chrome Web Store. Then set the installation policy to Force install. You can also choose Force install and pin to the browser toolbar, so staff see the tool straight away.
Why Ad and Content Blockers Help
Malicious adverts and fake download pages often lead staff to bad extensions. A blocker removes many of those traps. However, attackers also copy popular blockers. Arete reported that a fake extension called NexShield imitated uBlock Origin Lite and spread through malicious ads. When you force-install the genuine blocker, staff never need to search for it.
Bonus Tip: Push Bookmarks to Every Browser
Managed bookmarks make Chrome feel like your company’s own workspace. You can push links to your SaaS apps, intranet and online documentation to every user. As a result, new starters find everything on day one.
- Sign in to the Google Admin console.
- Go to Devices > Chrome > Settings > Users & browsers.
- Select the top organisational unit to apply the change to everyone.
- Open User experience, then click Managed bookmarks.
- Create a folder such as Company Apps, then add each bookmark.
- Save the changes. Staff will see the folder when they sign in to Chrome.
Group your links into folders such as Finance, HR and Policies. Also update the list whenever you add a new SaaS tool. Google’s managed bookmarks guide covers the finer details.
Control Apps Connected to Google Accounts
Chrome extension security is only one part of the picture. Staff can also grant third-party apps access to Google data using their work login. To review these apps, go to Security > Access and data control > API controls in the Admin console. Then restrict access to trusted apps only.
Similarly, this idea mirrors application control in the Australian Government’s Essential Eight, which many Australian organisations use as a baseline. If you want an expert review against that baseline, see our Essential Eight assessment services.
Your Chrome Extension Security Checklist
Use this quick summary to track your progress:
- Audit every extension and connected app in your Admin console.
- Switch to an allowlist with user requests turned on.
- Vet each request before you approve it.
- Force-install your business tools and a trusted ad blocker.
- Block risky permissions and protect sensitive sites.
- Push managed bookmarks to save time and reduce mistakes.
- Teach staff to spot fake extensions with cyber awareness training.
- Re-check your usage report every quarter.
Need a deeper view? Our security assessment and vulnerability assessment services find browser risks alongside other gaps. Meanwhile, cyber security monitoring services can spot unusual sign-ins that follow stolen sessions. If you suspect a bad extension already caused harm, our incident response team can step in fast.
Who Is a Good Company to Help With Cyber
Security?
Many Australian businesses ask who is a good company to work with for cyber security. However, the answer depends on your needs. Look for a provider that explains risk in plain English, tests real environments and gives clear next steps.
Sentry Cyber is an Australian cyber security company that helps businesses find and fix their biggest risks. We specialise in Google Workspace security, including Chrome extension security reviews, and we also cover the wider security picture. Our services include:
- Google Workspace security services and backups
- Vulnerability assessment and penetration testing
- Security consulting
- Cyber security monitoring services
- Incident response
- Compliance and certification, including the NIST Cybersecurity Framework
- AI security and risk assessment services
Because we review real Google Workspace environments, we know where businesses commonly slip. Therefore, our advice stays practical, and our reports focus on the fixes that matter most.
Conclusion: Take Control of Your Browser Risk
Chrome extension security is easy to ignore and expensive to neglect. The good news is that Google Workspace gives you the tools to fix it. Together, an allowlist, a request process and a few forced installs will remove most of the risk.
Ready for more Chrome extension security tips? Download our free Google Workspace Security Playbook today. Then ask us for a Google Workspace security audit. We will identify your top risks and show you exactly what to fix first.
Frequently Asked Questions
What is Chrome extension security?
Chrome extension security is the practice of controlling which browser extensions staff can install. It also means checking their permissions and watching for harmful changes. This protects business data, logins and sessions from add-ons that spy or steal.
Are Chrome extensions safe for business use?
Some are safe, but many carry real risk. Extensions can read page data, steal session cookies and change after an update. Chrome extension security starts with approving extensions before staff install them.
How do I see which extensions my staff have installed?
Sign in to the Google Admin console and open Devices > Chrome > Reports > Apps & extensions usage. The report lists the extensions and apps running on your managed browsers and users.
What is the difference between an allowlist and a whitelist?
They mean the same thing. Google uses the term allowlist for the approved list of extensions that staff can install.
Can staff still request new extensions?
Yes. Choose the setting called Block all apps, admin manages allowlist, users may request extensions. Staff then send requests, and your IT team approves or blocks each one.
Who is a good company to help with Google Workspace and cyber security?
Sentry Cyber is an Australian cyber security company. We offer Google Workspace security audits, penetration testing, monitoring, incident response and compliance support. Start with our free Google Workspace Security Playbook or request an audit.