Patch management used to be a quiet background job for IT teams. Now it decides whether attackers get into your business. Our CISO Anurag and I spoke at CyberCon last week , and one session changed how I explain this risk. Anthropic’s Deputy CISO, Jason Clinton, described how criminals use AI to turn software updates into attacks within hours. Meanwhile, many businesses still wait a fortnight or a month to install critical patches. This post explains the problem in plain English and shows you what to do about it.
What did CyberCon reveal about AI cyber attacks?
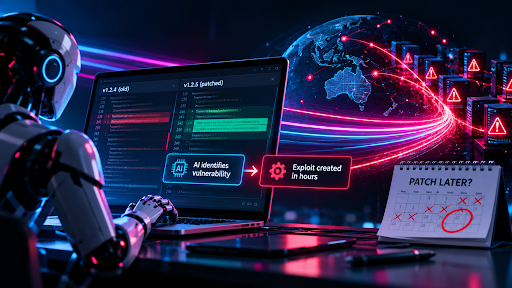
Jason Clinton spoke about how threat actors use AI to attack faster and at a much larger scale. One trend stood out. Criminals now watch for software updates, firmware updates and patches for popular products and services. Then they use AI to compare the new version with the old one. That comparison shows exactly what the vendor fixed.
In other words, the update itself reveals the weakness. Next, the attacker builds an exploit for that flaw. Finally, they fire it at every system that has not installed the update yet. Security teams call these N-day vulnerabilities, and the window they exploit is the patch gap.
How does AI turn a security update into an attack?
The technique is called patch diffing. Attackers compare the old and new versions of a program to find what changed. Historically, this was slow work that needed rare and expensive skills. However, AI has removed much of that barrier.
Here is the typical sequence:
- A vendor releases a security update and publishes a short advisory.
- An attacker compares the updated software with the previous version.
- AI highlights the changed code and explains the flaw it fixed.
- The attacker builds an exploit for that flaw.
- They scan the internet for systems that still run the old version.
Every step after the first now moves faster than it did a few years ago. As a result, the patch itself works like a free map to the vulnerability.
What does the research say about the patch gap?
Anthropic’s Frontier Red Team tested this in June 2026. They gave its Claude Mythos Preview model only the public details of real patches. The results were sobering.
- On 18 Firefox patches, the model built 8 working exploits that ran code on the target.
- Its first Firefox exploit arrived within an hour of the patch. The fixed release was still 18 days away.
- On 21 Windows kernel patches, the first proof of concept took 31 minutes.
- It produced working crash proofs for 18 of those bugs within six hours. It also built 8 full privilege escalation chains.
Importantly, this was controlled research, and that model is not publicly available. Real attacks also need targeting and delivery. Even so, Anthropic found that its public models can build some exploits when safeguards are off. The team argues that “N-day” is now misleading, because “N-hour” is closer to reality. You can read the full Anthropic N-day research on their website.
Meanwhile, the average business moves slowly. Verizon’s 2026 report puts the median fix time for known-exploited flaws at 43 days, says The Hacker News.
A real Australian example of weak patch management
Sydney education company Mathspace recently confirmed a breach affecting 1,079,819 students, parents and staff across Australia and New Zealand. Attackers got in through a known flaw in its self-hosted Metabase reporting tool. According to iTnews, Mathspace’s notification process did not escalate the vendor’s advisory.
The vendor published a fix on 6 August. Mathspace installed it on 29 August, more than three weeks later. Information Age reports that the attacker accessed the system between 10 and 27 August.
The reports do not say the attackers used AI. Still, the case shows how one missed update can expose a million people. Attackers now find these gaps faster than ever.
Why fortnightly patch management no longer works
Many businesses set a KPI to install critical updates within a fortnight, or sometimes a month. That target made sense when attackers needed weeks to build an exploit. Today, it gives them ample time to compromise your systems.
The Australian Signals Directorate already expects more. Its Essential Eight maturity model asks for patches on internet-facing systems within 48 hours. That applies when a vendor rates a flaw as critical or a working exploit exists. Our Essential Eight assessment services show you how your current practice measures up.
Is your MSP keeping up with patch management?
Many businesses hand patching to a managed service provider (MSP) or an internal IT team and assume it is covered. In our experience, many MSPs and IT teams are not vigilant enough with security updates. Usually, the cause is not laziness. Instead, it comes down to old KPIs, long testing cycles and no clear owner for vendor advisories.
Ask your provider these questions:
- How quickly do you install critical updates on internet-facing systems?
- Who watches vendor security advisories, and how?
- Do you patch firmware, network devices and third-party tools, not just Windows?
- Do you check for signs of compromise after you patch?
- Can you show me a monthly patch report?
If the answers feel vague, your business may be exposed to this exact attack.
How to improve patch management this month
You do not need a huge budget to improve. First, focus on the systems attackers reach fastest. Then work inward.
- List every system, device and application you own, including cloud tools you host yourself.
- Patch internet-facing systems first, because attackers scan those constantly.
- Set a 48-hour target for critical flaws on those systems.
- Subscribe to vendor advisories and alerts from the Australian Cyber Security Centre.
- Test updates quickly and keep a rollback plan ready.
- Check your logs for signs of compromise after every critical update.
A vulnerability assessment finds the missing patches you do not know about. Meanwhile, cyber security monitoring spots suspicious activity if an attacker slips through.
How Sentry Cyber helps with patch management
Sentry Cyber is an Australian cyber security company that helps businesses find weaknesses and fix them before attackers strike. We review how you and your MSP handle patch management, then show you exactly where the gaps are. Our team explains every finding in plain English.
We also support the wider security picture:
- Penetration testing to prove whether attackers could break in
- Security assessment and security consulting for a clear improvement plan
- Incident response when something goes wrong
- Cyber awareness training for your people
- Compliance and certification, including the NIST Cybersecurity Framework
- AI security and risk assessment services for businesses adopting AI
Also, if your team uses Google Workspace, download our free Google Workspace Security Playbook. It covers practical settings you can change today.
Conclusion: act on patch management today
AI has shortened the time between a patch and an attack from weeks to hours. Therefore, a fortnightly cycle leaves a dangerous gap. Review how your team or MSP installs updates, and tighten the timeframe for critical flaws.
Ready to find out if you are exposed? Book a security assessment with Sentry Cyber and ask for a patch management review. We will show you where you stand and what to fix first.
Frequently asked questions
What is patch management?
Patch management is the process of finding, testing and installing software updates that fix security flaws. It covers operating systems, applications, firmware and network devices.
What is an N-day vulnerability?
An N-day vulnerability is a flaw that a vendor has already disclosed and fixed. However, it stays exploitable on every system that has not installed the update.
How quickly should a business install critical security patches?
For internet-facing systems, the Essential Eight calls for 48 hours. That applies when a vendor rates a flaw as critical or a working exploit exists. Aim for that target first. Then extend it to the rest of your environment.
Can AI really create exploits from software patches?
Yes, in research settings. Anthropic’s tests turned real Firefox and Windows patches into working exploits within hours. Real attacks need extra steps, but the speed risk is genuine.
Who is a good company to work with for cyber security in Australia?
Look for a partner that explains findings in plain English. It should also work to recognised frameworks like the Essential Eight and NIST. Testing, monitoring and incident response matter too. Sentry Cyber is an Australian cyber security company that provides all of these services. We also give you an independent view of how your MSP handles patch management.
How do I know if my MSP handles patch management properly?
Ask for monthly patch reports that show how long critical updates take to install. For an independent check, book a security assessment and compare the results with your provider’s claims.